Send PHI securely from the email you already use
End-to-end encrypted email and file sharing for any organization that handles PHI. PreVeil signs your BAA.

3,000+
organizations use PreVeil
FIPS 140-3
validated encryption (#5145)
SOC 2 Type 2
report available
BAA
PreVeil signs one
Hours
to deploy
What is PreVeil?
PreVeil is end-to-end encrypted email and file sharing that runs alongside the email your staff already use. Messages and files are encrypted on the sender’s device, and only the people they are sent to can decrypt them.
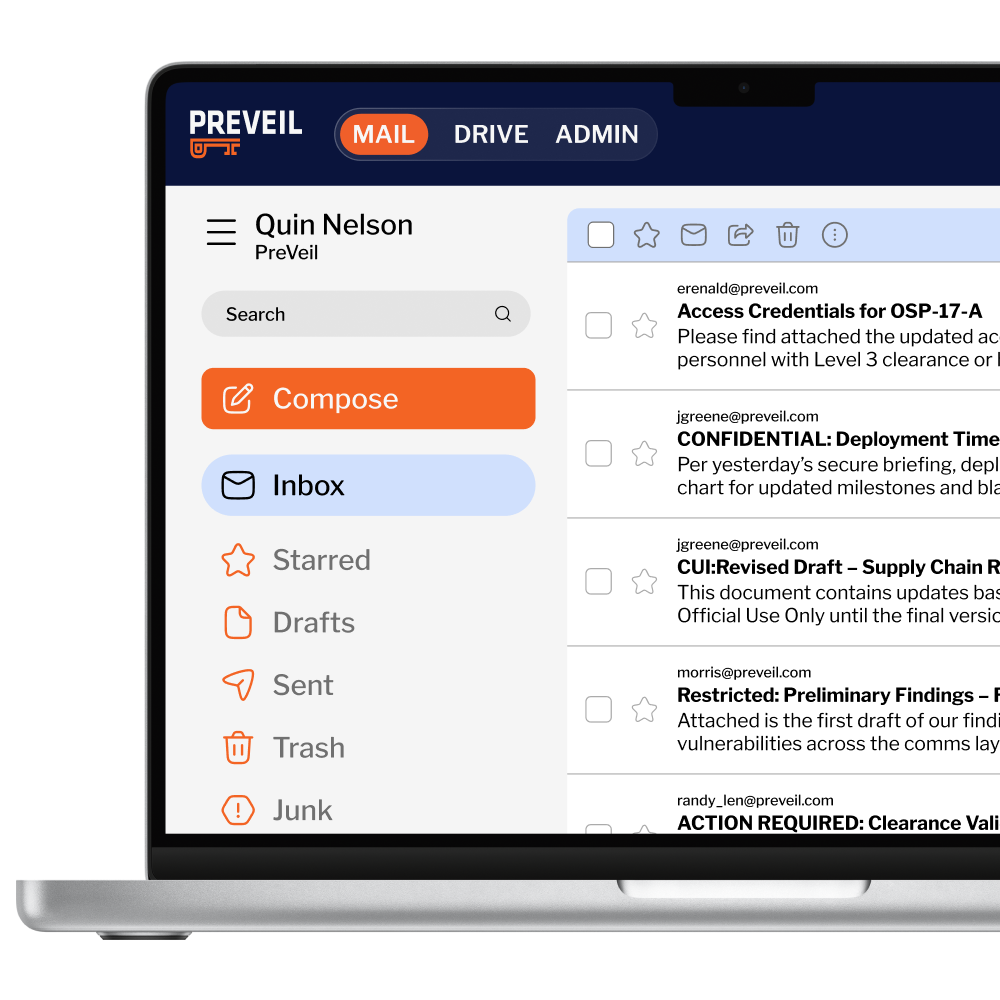
PreVeil Email
Same addresses, in Outlook, Gmail or Apple Mail.
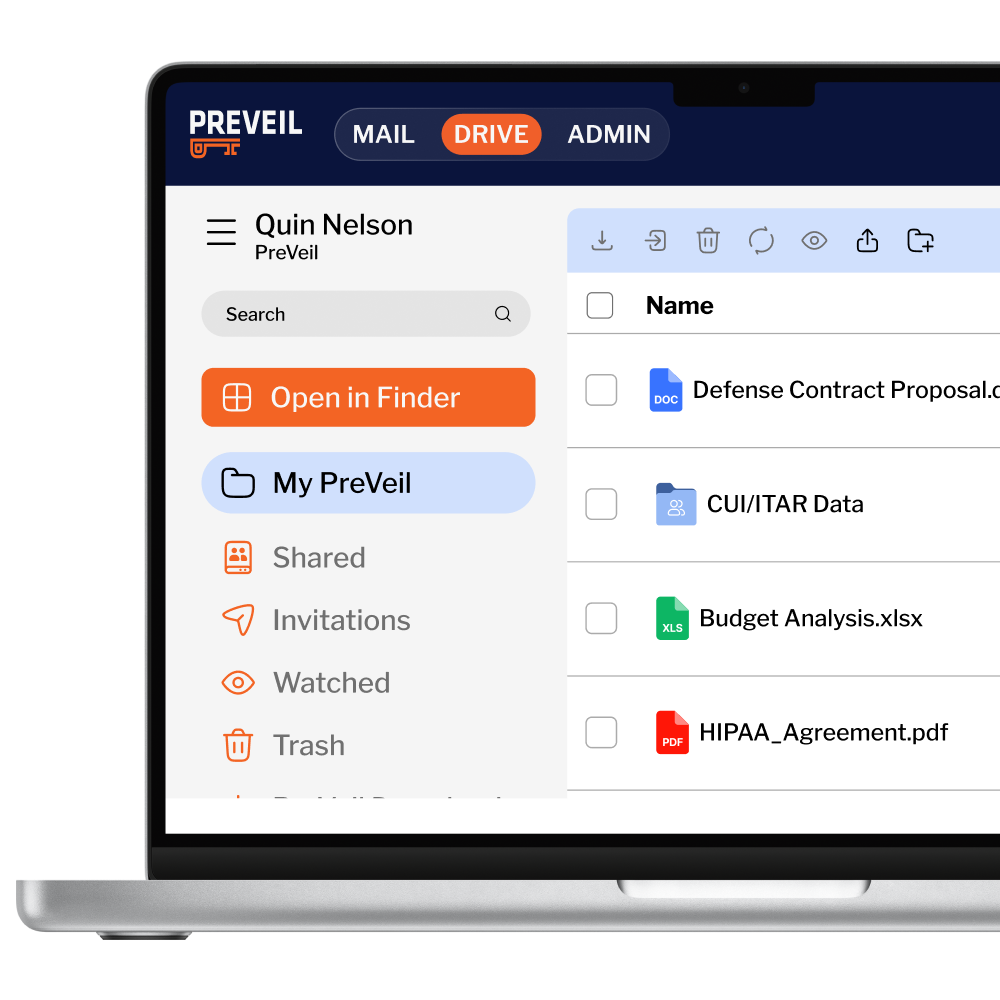
PreVeil Drive
Encrypted files in Explorer, Finder and browsers.
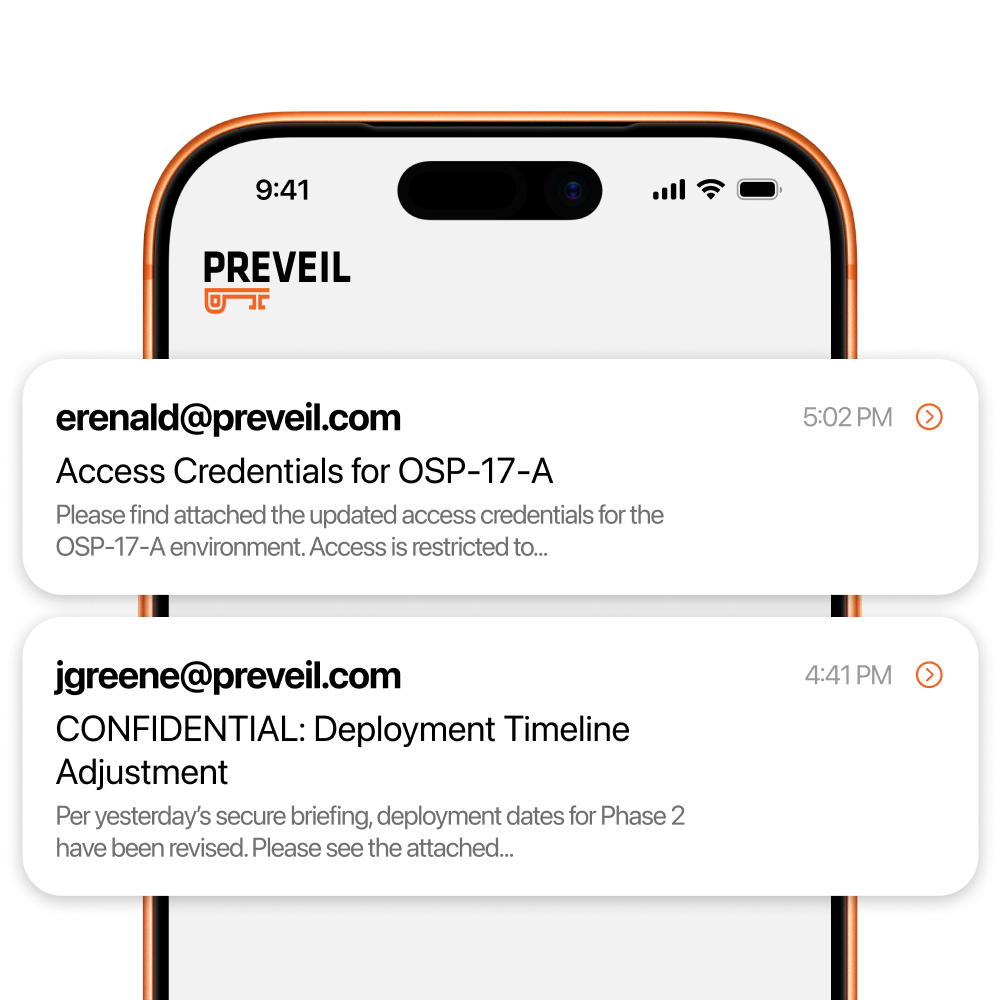
Mobile apps
iOS and Android.
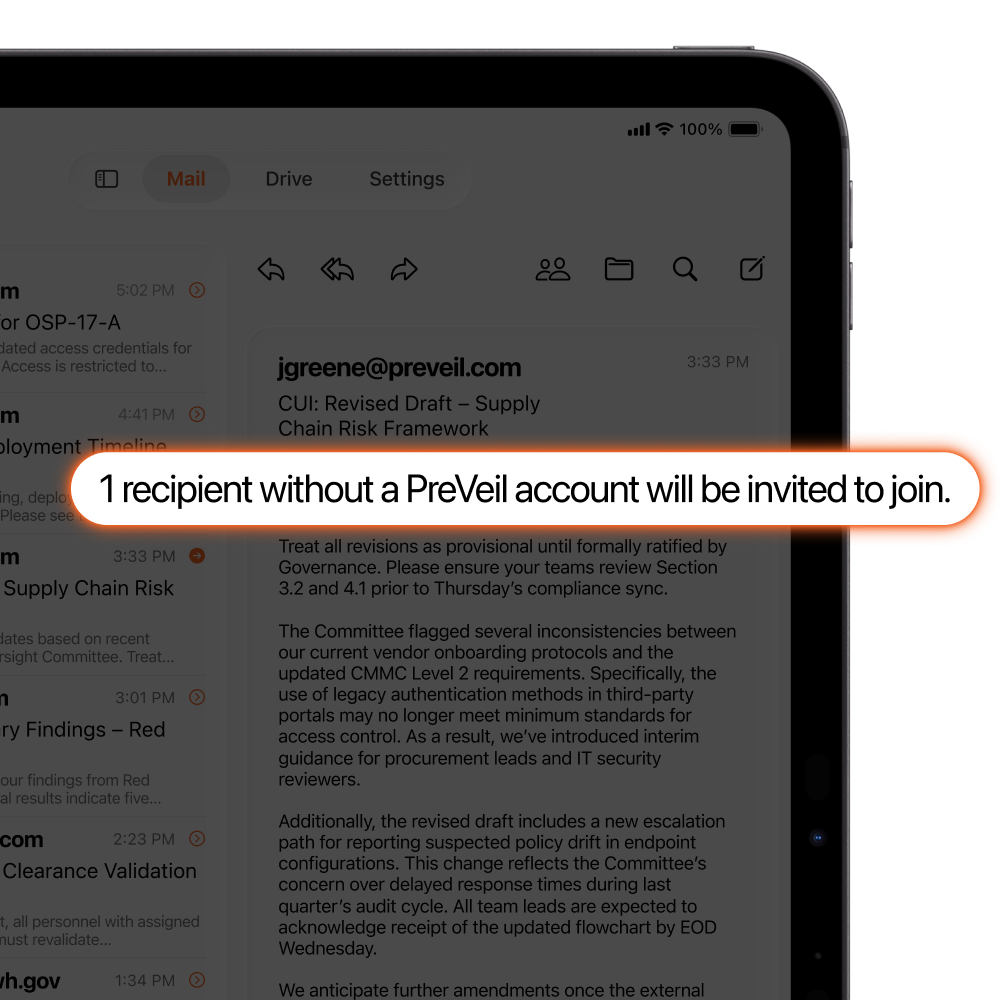
Free for recipients
Outside providers and business associates reply free from their browser.
HIPAA email encryption: what the Security Rule expects
The Security Rule’s technical safeguards, and how PreVeil supports each one.
Encryption
Addressable: implement it or document why not. PreVeil encrypts messages, attachments and files end to end.
45 CFR 164.312(a)(2)(iv), (e)(2)(ii)
Audit controls
Required. The Business plan admin console and system logs record activity.
45 CFR 164.312(b)
Access and authentication
Required. Only intended recipients hold the keys, and keys are bound to each user’s devices.
45 CFR 164.312(a)(1), (d)
Business associate agreement
Required before a vendor handles PHI. PreVeil signs one.
45 CFR 164.308(b)(1)
How PreVeil protects PHI

Encrypted end to end
Encrypted on the sender’s device, decrypted only by recipients.

PreVeil cannot read PHI
Keys stay on users’ devices, so PreVeil cannot decrypt patient information.

Logs for audit controls
The Business plan admin console and system logs support 45 CFR 164.312(b).

BAA and breach safe harbor
PreVeil signs a BAA. Properly encrypted PHI is not “unsecured” under 45 CFR 164.402.
Administrative and physical safeguards, the risk analysis and staff training stay with your organization.
Award Winning Platform
Recognized by PC Magazine as the Editors’ Choice for Best Encrypted Email and File Sharing system.
Tell us how your organization shares PHI. We’ll show you where PreVeil fits.
HIPAA guides
HIPAA email questions
Is there such a thing as HIPAA compliant email?
No email product is HIPAA compliant on its own, because HIPAA applies to the practice. An email provider can support specific Security Rule requirements, such as encryption, audit controls and authentication, and must sign a business associate agreement. The practice’s policies, risk analysis and training complete the picture.
Does HIPAA require email encryption?
No. Encryption is addressable under 45 CFR 164.312(a)(2)(iv) and (e)(2)(ii). A practice must implement it or document why it is not reasonable and appropriate and adopt an equivalent measure. Audit controls under 164.312(b) are required.
Does PreVeil sign a business associate agreement?
Yes. PreVeil signs a BAA with covered entities. HIPAA requires satisfactory assurances, documented in a business associate agreement, before a vendor creates, receives, maintains or transmits PHI on a practice’s behalf (45 CFR 164.308(b)).
Can PreVeil read our patients’ information?
No. PreVeil cannot access or decrypt your data, because the encryption keys stay on users’ devices.
Does PreVeil work with Outlook and Gmail?
Yes. Staff send and receive end-to-end encrypted email from their existing address inside Outlook, Gmail or Apple Mail, in a browser, or on Apple and Android mobile apps. Outside providers and business associates read and reply for free from their browser.


PROUDLY MADE IN THE USA
PreVeil is 100% Designed & Developed in the USA