On July 13, 2026, the Department of Defense suspended CMMC’s Phase 2 third-party assessment requirement. The suspension remains in effect but requirements to meet DFARS 7012 are unaffected. If 7012 appears in your contract, every obligation in it still applies exactly as it was before July 13th.
As Cyberlawyer Michael Gruden (Partner, Steptoe) stated at our 2026 CMMC Summit:
The seminal cybersecurity clause that has been around now for over a decade is DFARS 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting. That clause remains, even though there has been a FAR acquisition overhaul.
What is DFARS 7012?
DFARS 252.204-7012, “Safeguarding Covered Defense Information and Cyber Incident Reporting,” is the Department of Defense contract clause that puts the 110 NIST SP 800-171 security requirements into your contract. With 7012 in your contract, falling short of 800-171 is a failure to perform, not a gap against a guideline.
The clause protects one specific category of information: “covered defense information,” which on a DoD contract means your CUI — information the government gave you, or that you created for them in performing the work.
It has been in effect since the end of 2017, written in response to sustained cyberattacks against the Defense Industrial Base. CMMC was built to verify that you implemented those requirements — not to replace them. That is why the Phase 2 suspension changed nothing about 7012.
What does DFARS 7012 require?
The clause imposes three core obligations: safeguard the data, respond to incidents, and flow the requirements down.
1. Safeguard CUI (paragraph b). Implement the 110 NIST SP 800-171 controls. If a cloud provider stores, processes, or transmits CUI, it must meet FedRAMP Moderate or equivalent and support paragraphs (c)–(g).
2. Respond to incidents (paragraphs c–g). Report a cyber incident within 72 hours of discovery (c), submit isolated malware to the DoD Cyber Crime Center — not to your Contracting Officer (d), preserve forensic images and monitoring data for 90 days from submitting the report (e), provide forensic access on request (f), support a damage assessment (g).
3. Flow it down (paragraph m). If a supplier will handle CUI or provide operationally critical support, the clause goes into their subcontract unaltered — subcontracts for commercial products and services included. The one exception is a supplier of commercial off-the-shelf (COTS) items only.
Do I have to comply with FedRAMP standards as a DoD contractor?
DFARS 7012 requires that any cloud-service-provider (CSP) touching your CUI to meet the FedRAMP Moderate baseline or an equivalent standard. In practice, that makes FedRAMP Moderate equivalency a pass-through requirement for nearly every contractor. As cyberlawyer Michael Gruden stated at our 2026 CMMC Summit:
If you have CUI in the cloud, it must be in an environment that has been certified by FedRAMP and meets the FedRAMP moderate baseline or its equivalency. And when I say equivalency, I mean the DoD issued a deviation allowing for an equivalency to be met for certain cloud offerings that also meet the requirements that haven’t gone through formal certification. This is really critical when you’re thinking through your IT infrastructure, because it’s both your local networks and your cloud security requirements.
The requirement itself comes from DFARS 252.204-7012(b)(2)(ii)(D). In a December 21, 2023 memo, the DoD CIO defined what “equivalent” actually means. A provider claiming equivalency must:
- Demonstrate 100% compliance with all FedRAMP Moderate baseline controls — now referred to as Class C — with no outstanding POA&Ms
- Be assessed by an independent, authorized FedRAMP third-party assessment organization (3PAO). Self-attestation is not permitted.
- Submit a complete Body of Evidence (BOE) for review to the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC), the DoD’s highest assessment authority
How do I know if my cloud provider is really FedRAMP equivalent?
Use those three criteria noted above as your checklist. Concretely, ask any provider handling your CUI:
- Are you FedRAMP Moderate authorized, or claiming equivalency? (Both can satisfy the clause; the evidence standard for equivalency is what trips providers up.)
- Who performed your assessment, and are they an authorized 3PAO? Can you name them?
- Do you have outstanding POA&Ms against any Moderate baseline control?
- Has your Body of Evidence been submitted to and reviewed by DIBCAC?
- Do you meet 7012 (c)–(g)? A provider can be FedRAMP-compliant and still be unable to support your incident-reporting and forensic obligations.
- Will you provide a Customer Responsibility Matrix (CRM) showing which controls you cover, which you share, and which remain entirely yours?
If a provider cannot answer these in writing, treat the equivalency claim as unverified.
PreVeil was the first Cloud Service Provider to meet the DoD’s updated FedRAMP Moderate Equivalency criteria, maintaining a compliance program across all 325 FedRAMP Moderate/Class C controls, validated annually by independent accredited assessors, with a Body of Evidence attested to by an independent, credible, professional source. We also meet each of the five 7012 (c)–(g) requirements, and publish a statement documenting how.
Do all my cloud services need to be FedRAMP authorized?
The test of which of your systems needs FedRAMP authorization is whether the system touches CUI.
DFARS 7012 attaches the FedRAMP Moderate (or equivalent) requirement to cloud service providers that store, process, or transmit CUI. Nothing else pulls a system onto the FedRAMP path.
However, not needing FedRAMP authorization is not the same as being out of scope. A Security Protection Asset such as Threatlocker, stays in your CMMC assessment boundary and gets assessed — it just isn’t assessed against FedRAMP.
How quickly must I report a cyber incident to the DoD?
An organization must report an incident to the DoD within 72 hours. This is the most operationally urgent part of the clause, and the part contractors most often discover they are unprepared for.
Paragraphs (c) through (g) specify five distinct obligations:
Four things to settle before you need them:
The 72-hour clock starts at discovery, not confirmation. If monitoring flags behavior consistent with unauthorized access to a CUI system, the clock runs while you investigate. There is no grace period for internal approvals, and an unnecessary report carries no penalty. A missed deadline does.
You cannot report without a medium assurance certificate. DIBNet requires a DoD-approved medium assurance certificate from an External Certificate Authority . Identity verification takes time and money, and a certificate applied for after an incident will not arrive inside 72 hours. Apply now, and designate someone to hold it. If an incident happens before your certification arrives, DC3’s DCISE team can provide an escalation path.
Preservation conflicts with your containment instinct. The reflex after discovering ransomware is to isolate, wipe, and restore from backup. Paragraph (e) requires forensic images first. Put an imaging step ahead of remediation, and keep the right telemetry for a full 90 days.
Your cloud provider has to be able to do this with you. Paragraphs (f) and (g) reach into the cloud environment holding your CUI. If the DoD requests forensic access or runs a damage assessment, your provider has to produce images, logs, and access. One can meet the FedRAMP Moderate baseline and still support none of this. Ask in writing, before you need it.
What are my flow-down responsibilities under DFARS 7012?
What do I have to flow down to my subcontractors?
As PreVeil’s Christopher Sanfilippo put it at CMMC Day 2026: “The trigger is the type of information your supplier receives or generates while performing the work, not whether you have a subcontract. If a supplier never handles CUI, CMMC generally doesn’t flow down to them.”
So the question to ask about any supplier is whether they will receive, create, or touch CUI while doing the work. If they will, 7012 goes with it.
What does my subcontractor have to do?
A supplier that receives CUI takes on the same obligations you have — safeguard it, report incidents, preserve evidence — not a lighter version of them. The one addition: a supplier who passes CUI to their own vendors inserts the clause for them too.
What do I have to do as the prime?
Determine whether the work involves CUI. This is your job, not your supplier’s. If you cannot tell whether what you are sharing still carries that status, raise it with your contracting officer before you share it.
Insert the clause unaltered. The only permitted change is identifying the parties. You cannot soften it, and you cannot substitute your own cybersecurity terms for it.
Collect the incident report number. A supplier who has an incident reports to the Department of Defense directly, then gives you the incident report number the DoD assigns. Put a field for it in your supplier process.
Be prepared not to share. If a supplier will not accept the clause, CUI cannot go to them.
How far down the supply chain does 7012 go?
Flow-down is not a first-tier obligation — it follows the data. A tier-two supplier who receives CUI from your tier-one supplier takes on the same clause, and so does tier three. It stops at the last company that handles the information.
How do I know if DFARS 252.204-7012 applies to me?
The clause applies to any contractor whose systems process, store, or transmit CUI in performing a DoD contract. Your contract is where you find out.
As Dan Cerletti of Domestic Technical Services, an assessor, told our 2026 CMMC Summit: “The first thing I always recommend people do is look at your contracts. Do you have DFARS 7012 in it or DFARS 252.204-7012? That will indicate if you’ll be given or you will be creating CUI. If you don’t have that in there and you think you’re getting CUI, then talk to your contracting officer.”
If you are a subcontractor, the clause can reach you through your prime rather than from the DoD directly. The flow-down section above explains how.
What are the risks of non-compliance with DFARS 7012?
There are four distinct categories of risk:
Contractual. In a June 2022 memo, the DoD stated that failure to have or to make progress on a plan to implement NIST SP 800-171 requirements may be considered a material breach of contract, with remedies including withholding progress payments, foregoing remaining contract options, and terminating the contract in part or in whole. A missed 72-hour reporting window can be treated as a separate compliance failure from the incident itself, and your reporting track record can factor into future award decisions.
Legal. Organizations that misrepresent their cybersecurity posture face penalties under the False Claims Act. In FY2025, the Department of Justice recovered more than $52 million across nine cybersecurity-related False Claims Act settlements. Among them was $8.4 million paid by Raytheon Company, RTX Corporation and two Nightwing entities, resolving allegations that Raytheon and a then-subsidiary failed to implement required cybersecurity controls — including a system security plan — on an internal development system used for unclassified work on 29 DoD contracts and subcontracts between 2015 and 2021.
Companies should not think they are too small to be pursued. In June 2026, LOGZONE Inc., a Huntsville, Alabama contractor, agreed to pay $507,144 to resolve False Claims Act allegations covering two Navy contracts. The Defense Contract Management Agency assessed the company’s NIST SP 800-171 implementation and scored it -170, at the low end of a range running from -203 to 110.
Commercial. Primes are not waiting to get assessed themselves, and they are increasingly choosing suppliers who have chosen the same path. A contractor who cannot demonstrate compliance is the one who gets passed over. As Travis Goldbach of Coalfire Federal noted at our 2026 CMMC Summit:
When I speak with prime contractors, we have quite a few that are already and continuing to move forward with their own assessments, and they see certification as a competitive advantage, and they think that’s the same for their supply chain. It’s going to build the customer confidence… And it’ll also help out with better cyber insurance outcomes.
Operational: Operational risk is why the NIST 800-171 and DFARS 7012 standards were written. Dr. Ron Ross, who authored NIST SP 800-171, put the problem plainly at our 2026 CMMC Summit: “What happens when sensitive information goes over the fence to the contractors?” If an adversary gets it, “they can replicate that weapon system for a lot less money and a lot quicker. And we lose our technological advantage on the battlefield.”
Smaller suppliers are where that information is least defended, and attackers know it. In 2020, Visser Precision — a Denver manufacturer reported to make parts for Lockheed Martin, Boeing and SpaceX — was hit by DoppelPaymer ransomware. Visser did not pay, and the attackers posted a selection of stolen documents online, reportedly including material relating to Lockheed Martin military equipment. Visser is not a prime. It is a machine shop.
Prime or sub, the exposure is the same: downtime, recovery costs, stolen intellectual property, a ransom your company may not survive. That is what the 110 controls 7012 requires are there to guard against.
Does DFARS 7012 still apply during the CMMC Phase 2 suspension?
Yes. Full stop. DFARS 7012 is a contractual obligation that exists independently of the CMMC assessment program. The July 2026 suspension paused the requirement for third-party (C3PAO) assessment under CMMC Phase 2. It did not pause, waive, or modify anything in 7012.
This distinction matters. CMMC is the verification layer — the mechanism by which the Department confirms contractors did what they already agreed to do. DFARS 7012 is the obligation layer. Suspending verification does not remove the underlying duty, and it does not remove liability for misrepresenting your compliance.
Every obligation in the clause continues unchanged during the suspension — safeguarding, incident response, and flow-down alike, and your SPRS self-assessment score carries the same enforcement exposure it did before. Whether your organization chooses to pursue a third-party assessment or not during the pause is a separate business decision, driven by what your primes are asking for rather than by anything in 7012.
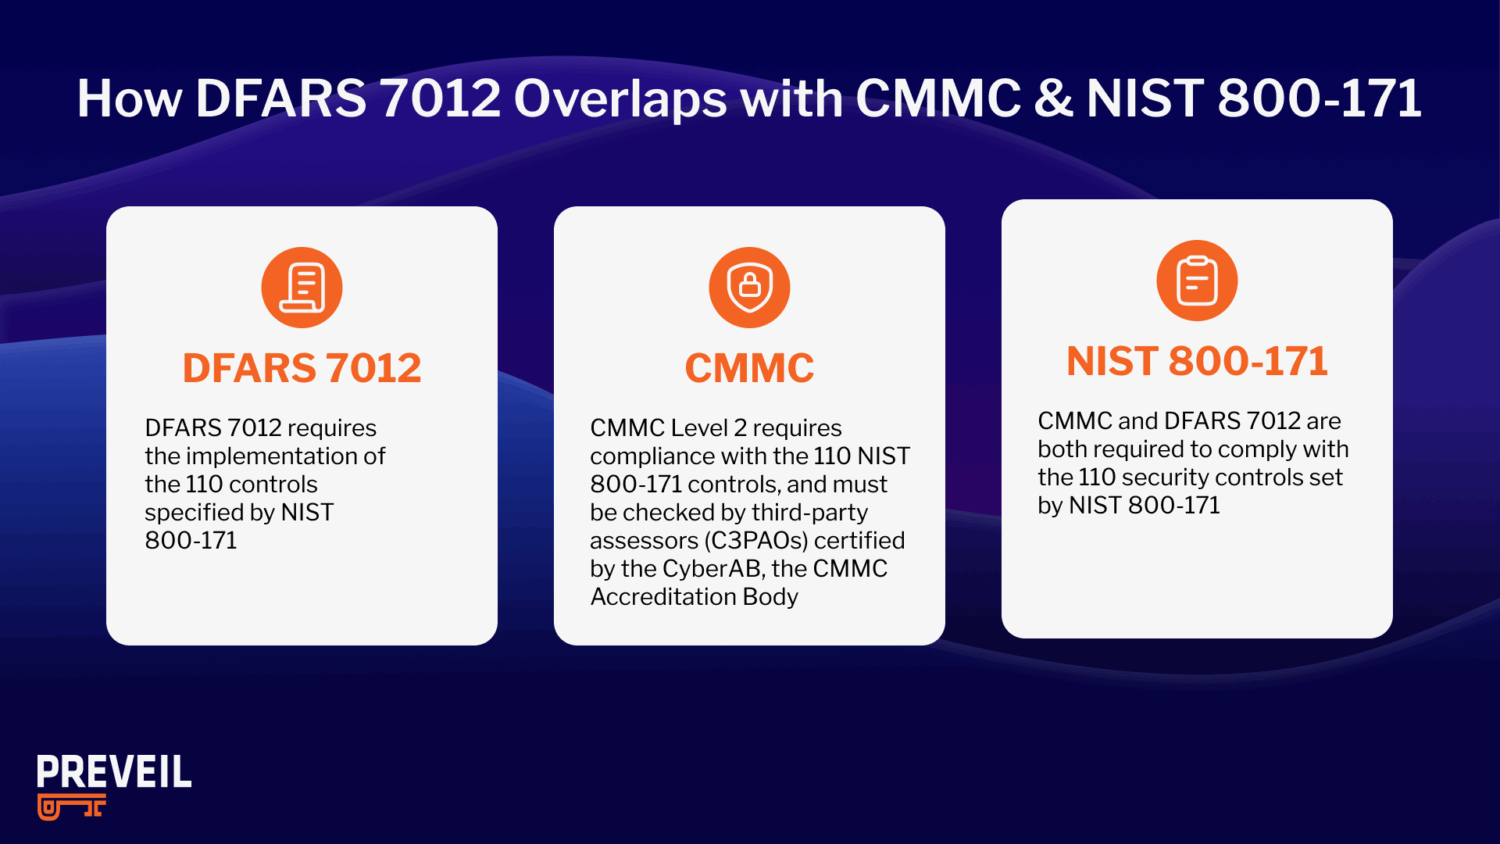
How do DFARS 7012 and CMMC Level 2 overlap?
DFARS 7012 requires implementation of the 110 controls in NIST SP 800-171. CMMC Level 2 — the minimum level for contractors handling CUI — requires compliance with those same 110 controls.
The difference is enforcement. Under 7012 alone, compliance was self-attested and inconsistently enforced. CMMC introduced independent verification by C3PAOs certified by the CyberAB. As DoD CMMC program leadership has put it, CMMC is the validation program confirming that contractors did what they already agreed to do in complying with NIST 800-171 on their networks.
Which is exactly why the Phase 2 suspension does not reduce your obligations. Verification was paused. The requirement it verifies was not.
What does DFARS 7012 compliance actually cost a small contractor?
Most of what people mean by “the cost of compliance” is CMMC cost — assessment fees, readiness work, and the size of your assessment boundary. 7012 itself carries no assessment fee. What it costs you is implementing the 110 controls and standing up incident response.
The variable that moves the total more than any other is scope. Every additional user, endpoint, and system inside your CUI boundary multiplies licensing, training, documentation and assessment cost — which is why isolating CUI handling to a small, defined set of users and systems, rather than hardening your entire organization, is the largest cost lever a small contractor has.
For line-item ranges and an estimate against your own environment, see our post on CMMC certification costs and our CMMC cost calculator.
How can defense contractors comply with DFARS 252.204-7012?
A sequence that works, in order:
- Confirm the clause applies. Search your active contracts for “DFARS 252.204-7012.”
- Scope your CUI boundary. Identify what CUI you handle and where it lives, then make that boundary as small as defensibly possible — this drives every downstream cost.
- Adopt a compliant platform for CUI. Email and file sharing are how CUI moves most often. Microsoft 365 Commercial cannot support CUI. Verify any provider against the FedRAMP checklist above, including 7012 (c)–(g).
- Develop your documentation. The SSP is foundational — no assessment succeeds without an accurate one. You will also need a Customer Responsibility Matrix from your CSP and any External Service Providers, plus policies and procedures per control family.
- Self-assess against NIST 800-171A’s 320 objectives, not 110 requirements and record your score. Where gaps remain, build a POA&M with resources, milestones, and completion dates.
- Stand up incident response. Obtain a medium assurance certificate, register your DIBNet point of contact, write the incident response plan (also required by NIST 800-171 §3.6), and confirm your logging retains 90 days of telemetry.
- Flow the clause down. Review subcontracts involving CDI or operationally critical support, determine whether the information retains CDI status, and include 7012 unaltered. Confirm your subs can meet it — if they can’t accept the clause, CDI can’t go to them.
- Keep going through the suspension. The assessment timing shifted. The work did not.
Get the full guide. PreVeil’s whitepaper, Complying with CMMC, has helped over 6,000 defense contractors work through exactly this sequence. It covers the required security controls, a detailed spreadsheet identifying the 102 of 110 controls PreVeil supports, and the current compliance timeline.
DFARS 7012 FAQs
Does DFARS 7012 still apply during the July 2026 CMMC Phase 2 suspension?
The suspension paused CMMC’s third-party assessment requirement. DFARS 7012 is a contract clause that operates independently of the CMMC rollout schedule, and none of its requirements were modified.
How quickly must I report a cyber incident?
Within 72 hours of discovery, via DIBNet at dibnet.dod.mil. The clock starts when you discover an incident may have occurred, not when you confirm it.
How long must I preserve evidence after an incident?
At least 90 days from the submission of your cyber incident report, covering images of all known affected systems and all relevant monitoring and packet capture data.
Does DFARS 7012 apply to subcontractors?
Yes. The clause requires flow-down of all 7012 requirements to subcontractors, unchanged except for the parties.
Is Microsoft 365 Commercial sufficient for DFARS 7012?
No. M365 Commercial does not meet the 7012 (c)–(g) incident reporting requirements, a fact Microsoft acknowledges. It cannot serve as your CUI boundary.
How do I verify a cloud provider is FedRAMP Moderate equivalent?
Ask for the three things the DoD CIO’s December 2023 memo requires: 100% compliance with the Moderate baseline with no outstanding POA&Ms, an assessment by an authorized independent 3PAO (not self-attestation), and a Body of Evidence submitted to DIBCAC.
Does an SPRS score still matter during the suspension?
Yes. Self-assessments and affirmations submitted to SPRS continue to carry False Claims Act exposure regardless of assessment timing.
Conclusion
PreVeil is the leading solution for DFARS 7012, NIST 800-171 and CMMC compliance and is trusted by more than 3,000 small and midsize defense contractors. In addition, over 100 PreVeil customers have achieved compliance with DFARS 7012/CMMC- validated by a perfect 110 score on their C3PAO or DoD assessment.
PreVeil supports 102 of the 110 NIST SP 800-171 controls, meets each of the five 7012 (c)–(g) requirements, and was the first CSP to meet the DoD’s FedRAMP Moderate Equivalency criteria. Because PreVeil deploys as an enclave alongside your existing Microsoft 365 or Google Workspace environment, only the users who handle CUI need licenses — which keeps both your compliance boundary and your cost as small as possible.
Start here: PreVeil’s guide Complying with CMMC has helped over 6,000 defense contractors understand what’s required and build a plan to get there — including a detailed spreadsheet of the 102 of 110 NIST SP 800-171 controls PreVeil supports.
Already know what you need? Talk to our compliance team about your specific environment and CUI boundary.

