Encrypted email for law firms with regulated clients
PreVeil answers your clients’ security terms for email and files, inside the Outlook or Gmail you already use.
3,000+
organizations use PreVeil
FIPS 140-3
validated encryption (#5145)
SOC 2 Type 2
report available
BAA
when the work involves PHI
Hours
to deploy
Your clients’ obligations reach your firm
Regulated clients pass their security terms to outside counsel.
Healthcare clients
A BAA when the work involves PHI, and direct Security Rule liability.
45 CFR 160.103; 164.308(b)(2)
Financial services clients
Encryption and MFA terms for counsel with access to nonpublic information.
23 NYCRR 500.11(b), 500.12, 500.15
Defense and federal contractors
Contract terms to protect the CUI clients share.
32 CFR Part 2002
Every client
Outside counsel guidelines, questionnaires, ABA Rule 1.6(c) and state breach laws such as New York’s SHIELD Act.
ABA Formal Op. 477R and 483
Clients ask often, and more often as a firm grows
27%
asked by clients for security requirements
41%
at firms with 10 to 49 lawyers
59%
at firms with 50 to 99 lawyers
29%
said their firm had a security breach
Source: ABA 2023 Cybersecurity TechReport
How PreVeil answers your clients’ terms
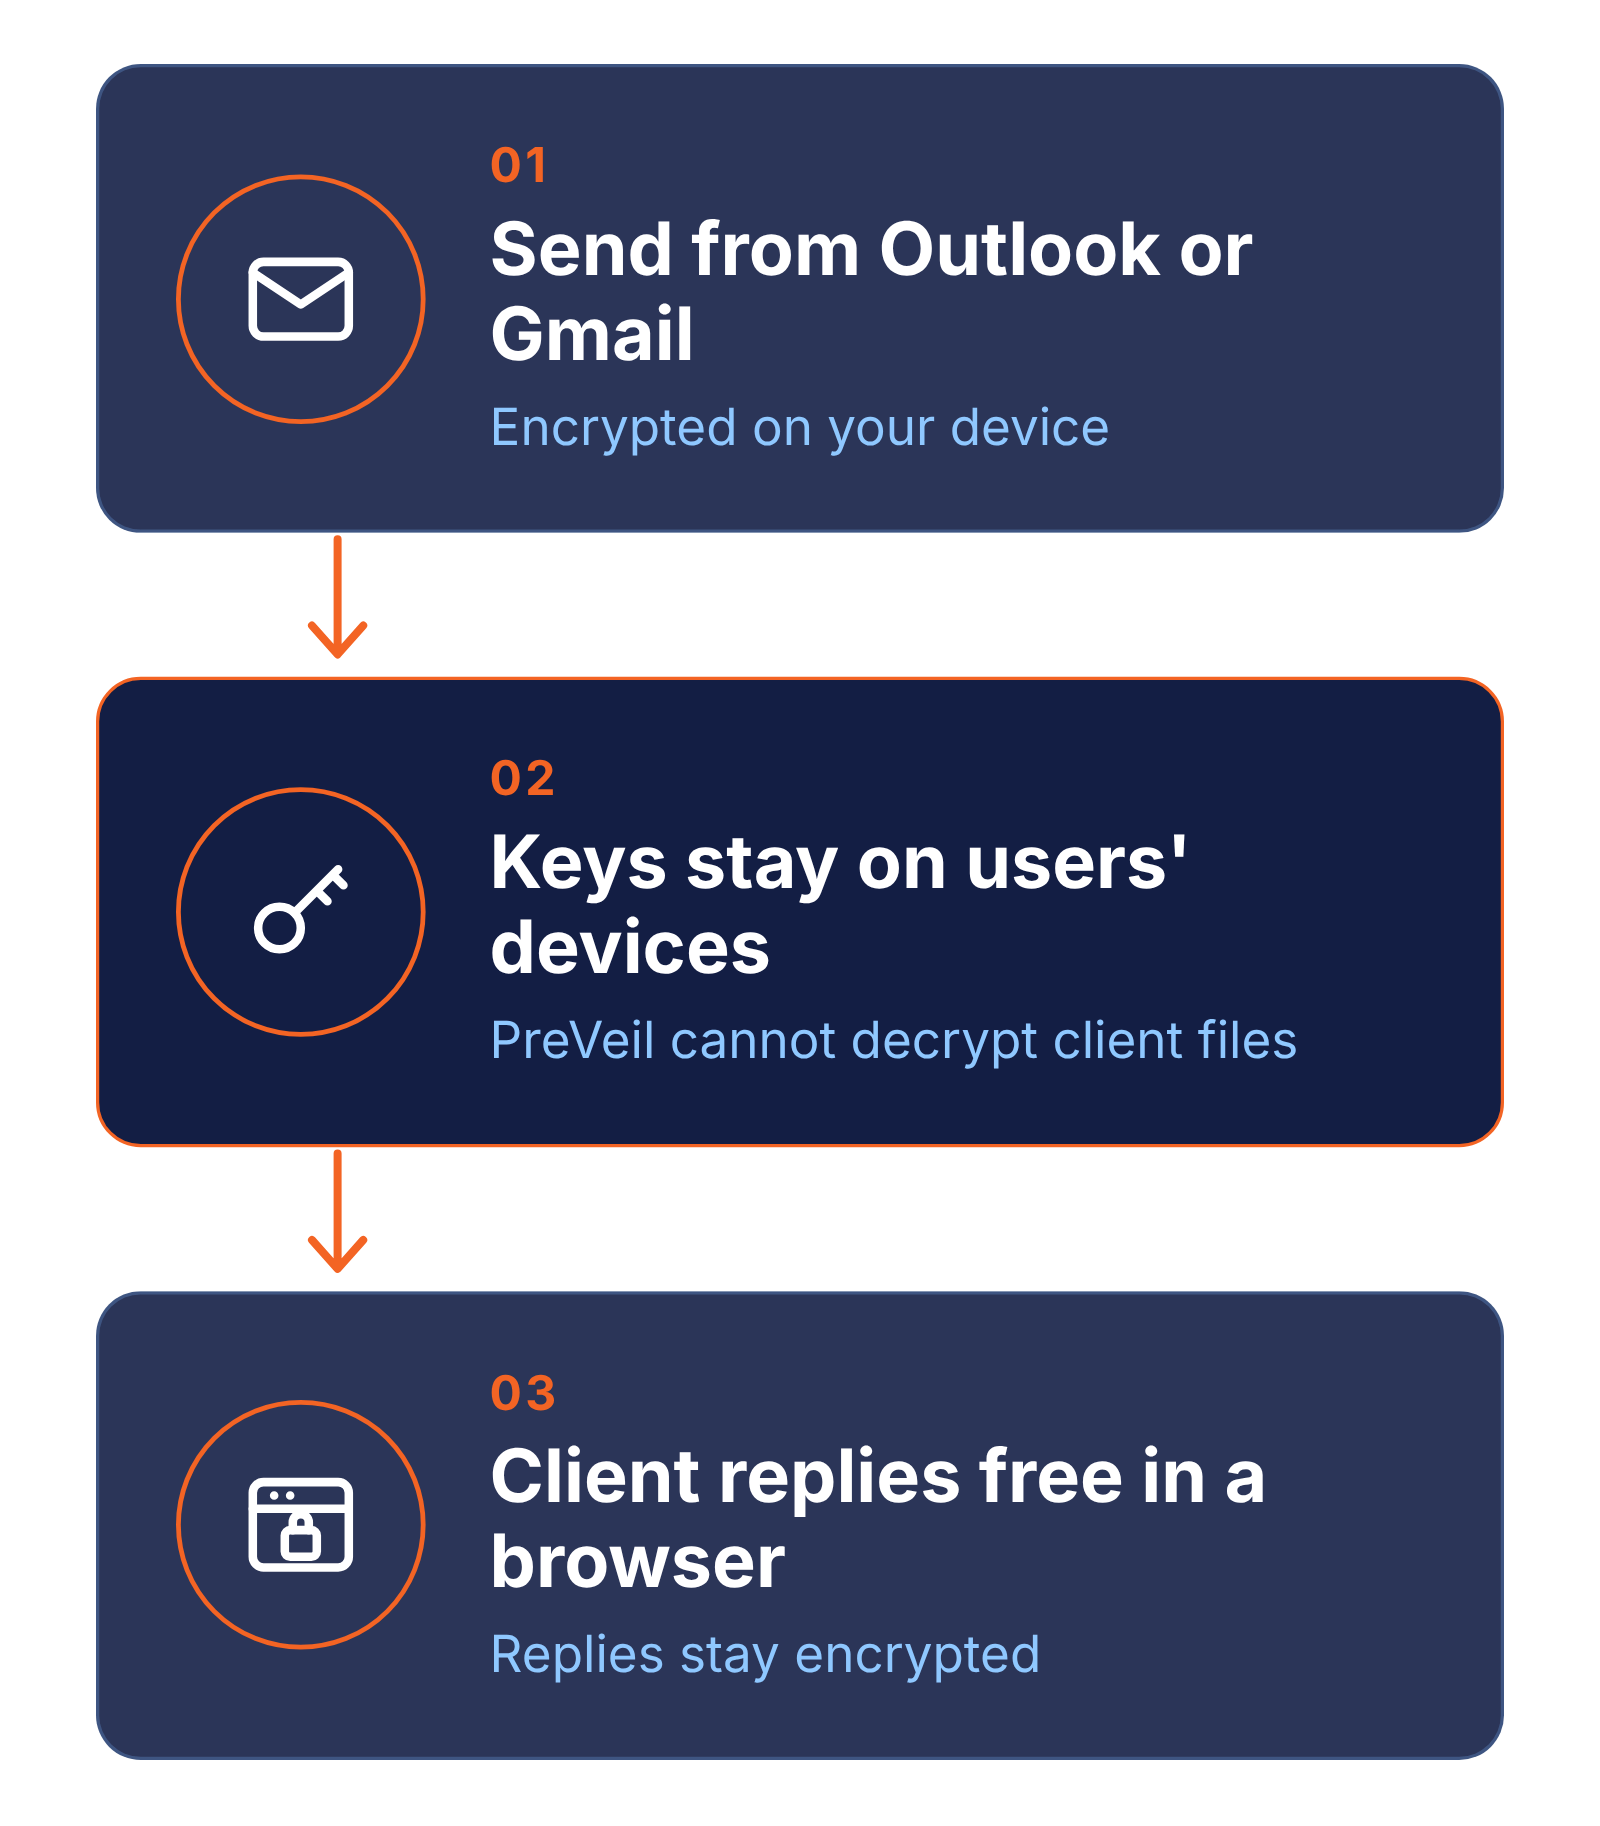

Encrypted end to end
Encrypted on the sender’s device, decrypted only by recipients. Supports ABA Op. 477R.

PreVeil cannot read client data
Keys stay on users’ devices, so PreVeil cannot decrypt client files.

Logs for vendor monitoring
Business plan admin console and activity logs support ABA Op. 483 monitoring and HIPAA audit controls.

BAA and CUI
A BAA when the work involves PHI. The CUI protection built for CMMC covers client CUI.
Policies, training and incident response stay with the firm.
Little changes for staff or clients
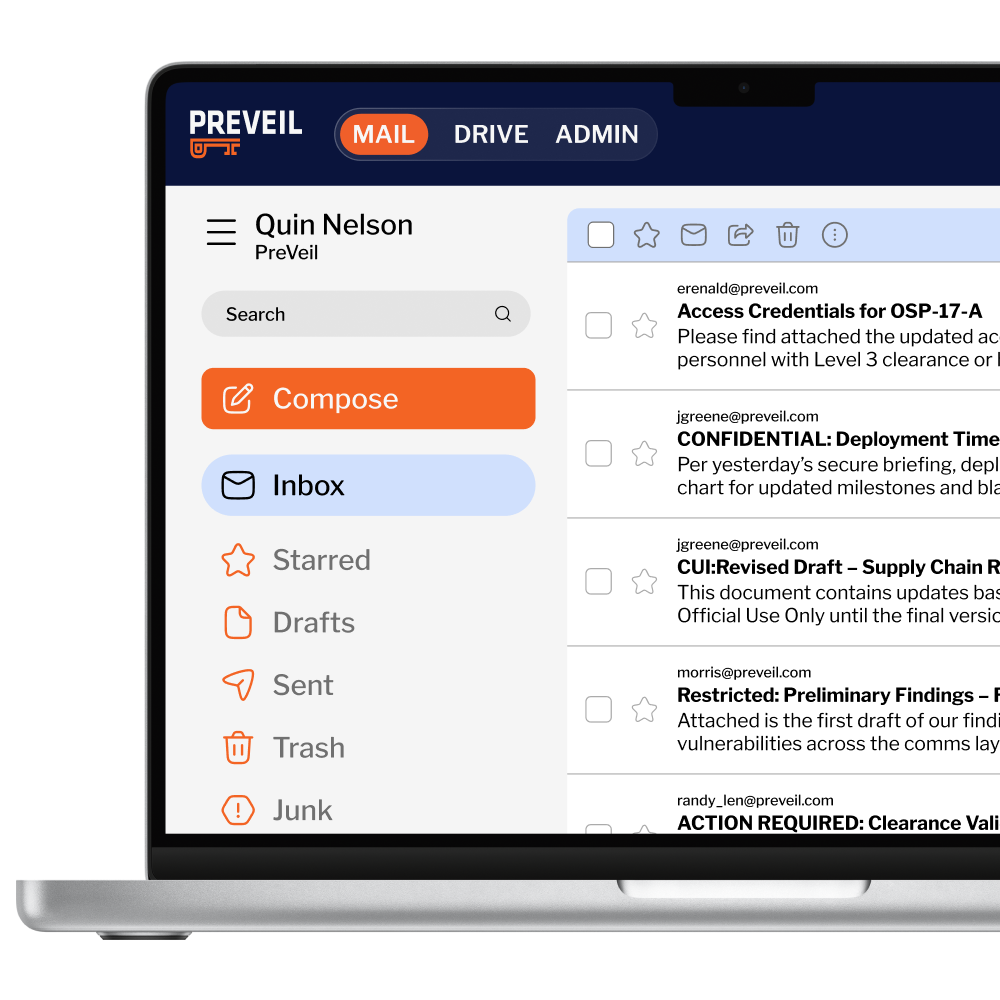
PreVeil Email
Same addresses, in Outlook, Gmail or Apple Mail.
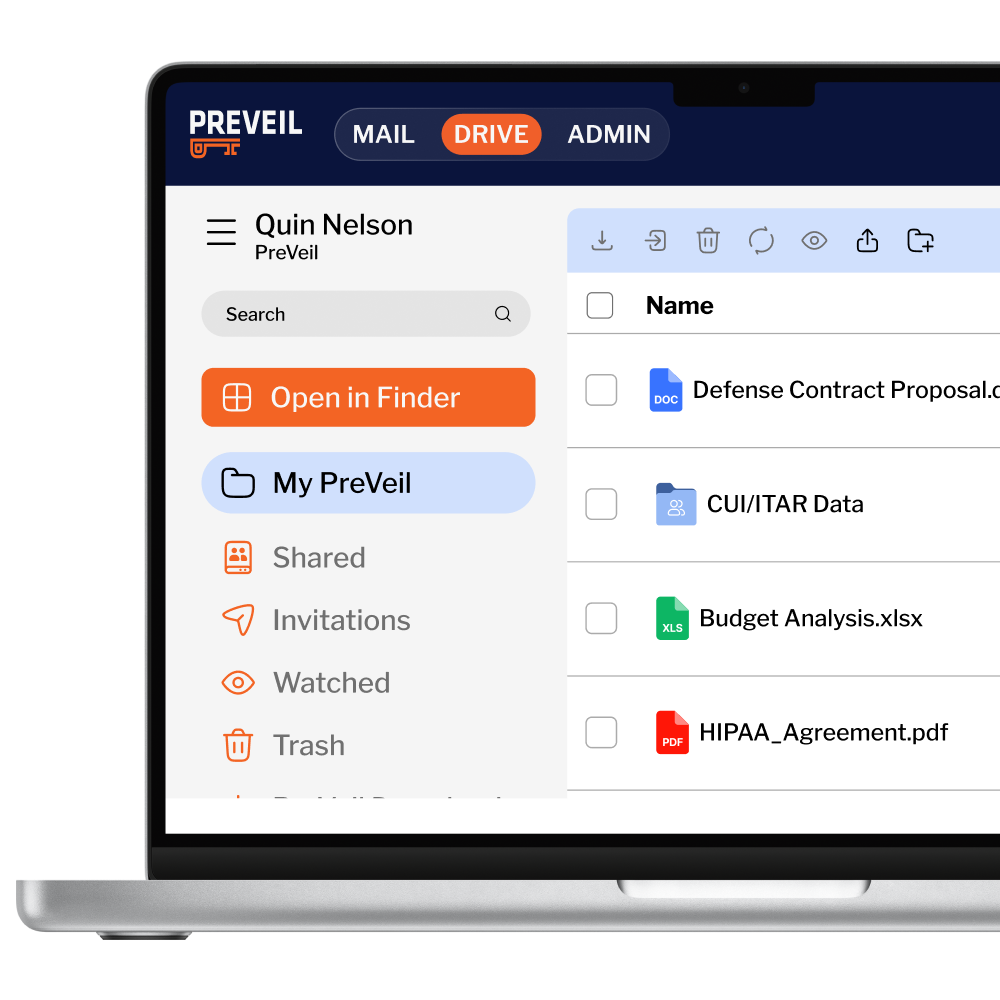
PreVeil Drive
Encrypted files in Explorer, Finder and browsers.
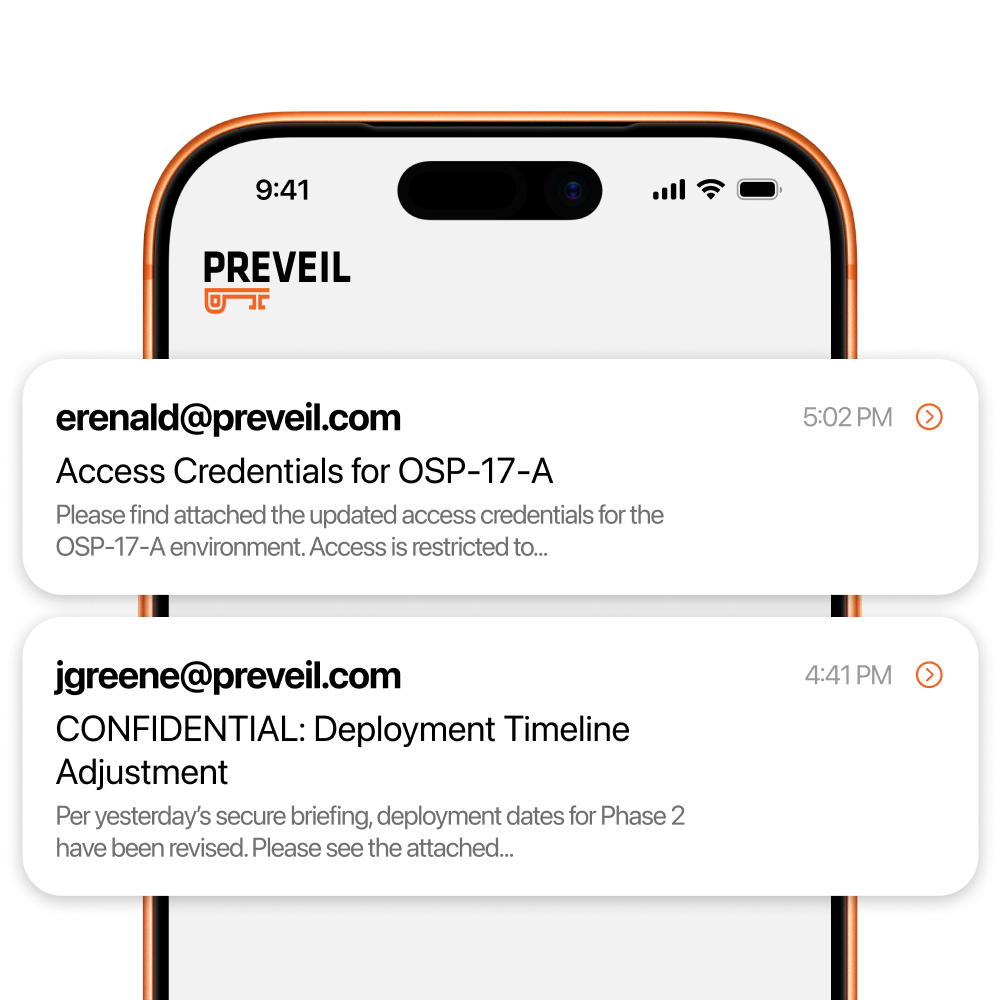
Mobile apps
iOS and Android.
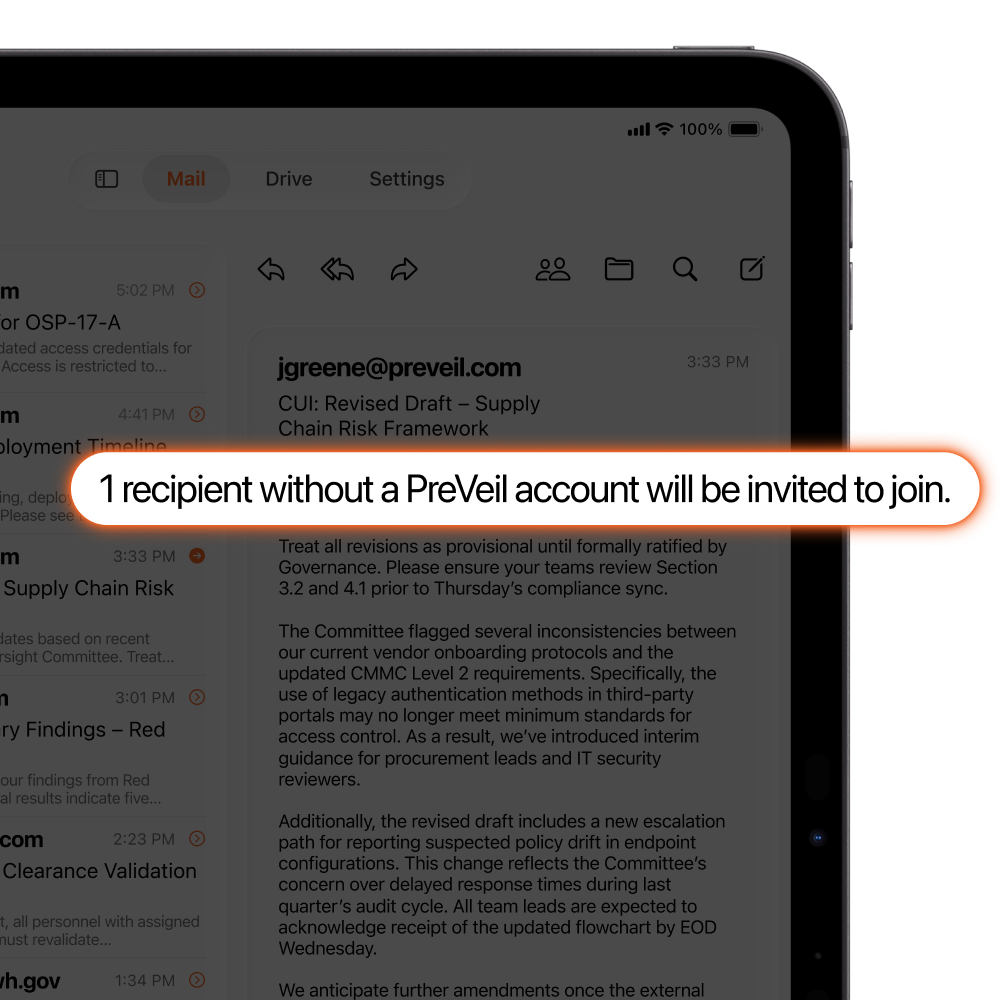
Free for clients
Clients reply free from their browser.
Easier & Less Expensive = A No Brainer
You don’t want to be on the front page after a breach; PreVeil meets NIST 800-171 … standards and was hands-down the easiest solution to use because it integrates seamlessly with our workflows, like Outlook.
DBL ultimately decided PreVeil is easier, less expensive, and therefore, a no brainer.
Jennifer Morris
Partner, Dunlap Bennett & Ludwig
Award Winning Platform
Recognized by PC Magazine as the Editors’ Choice for Best Encrypted Email and File Sharing system.
Tell us which clients send security terms. We’ll show you where PreVeil fits.
Guides for law firms with regulated clients
Questions from law firms
Does NYDFS Part 500 apply to law firms?
Not directly. NYDFS Part 500 never names law firms. It requires DFS-regulated companies to set guidelines for their service providers covering encryption and multi-factor authentication to the extent applicable (23 NYCRR 500.11(b)), and those terms reach outside counsel through the engagement.
Is my firm a HIPAA business associate?
A law firm is a HIPAA business associate when its legal services for a healthcare client involve access to protected health information (PHI). HHS lists an “Attorney whose legal services to a health plan involve access to PHI” as an example. The firm then signs a business associate agreement (BAA) with the client and needs assurances from its own vendors. PreVeil signs a BAA with law firms when the work involves PHI.
Does my firm have to meet CMMC to handle a client’s CUI?
No. Law firms are not required to meet CMMC. Controlled unclassified information (CUI) is a type of client data. Defense and federal clients often share CUI with outside counsel, and their contracts may require the firm to protect it.
Is a confidentiality disclaimer enough to protect client email?
No. A confidentiality disclaimer states an expectation, but it does not stop anyone with access to the message from reading it. With PreVeil, message contents and attachments are encrypted end to end, and only the sender and recipients can read them.
Can PreVeil read our clients’ files?
No. PreVeil cannot access or decrypt your data, because the encryption keys stay on users’ devices.
Sources for this page: 45 CFR 160.103 and 164.308 (eCFR); HHS business associates guidance; 23 NYCRR Part 500 Second Amendment text (DFS); ACC press release on the model controls, March 29, 2017 (https://www.acc.com/about/newsroom/press-releases/acc-issues-guidelines-law-firm-cybersecurity-measures); 32 CFR Part 2002 (eCFR); ABA Formal Opinions 477R and 483; ABA 2023 Cybersecurity TechReport.


PROUDLY MADE IN THE USA
PreVeil is 100% Designed & Developed in the USA