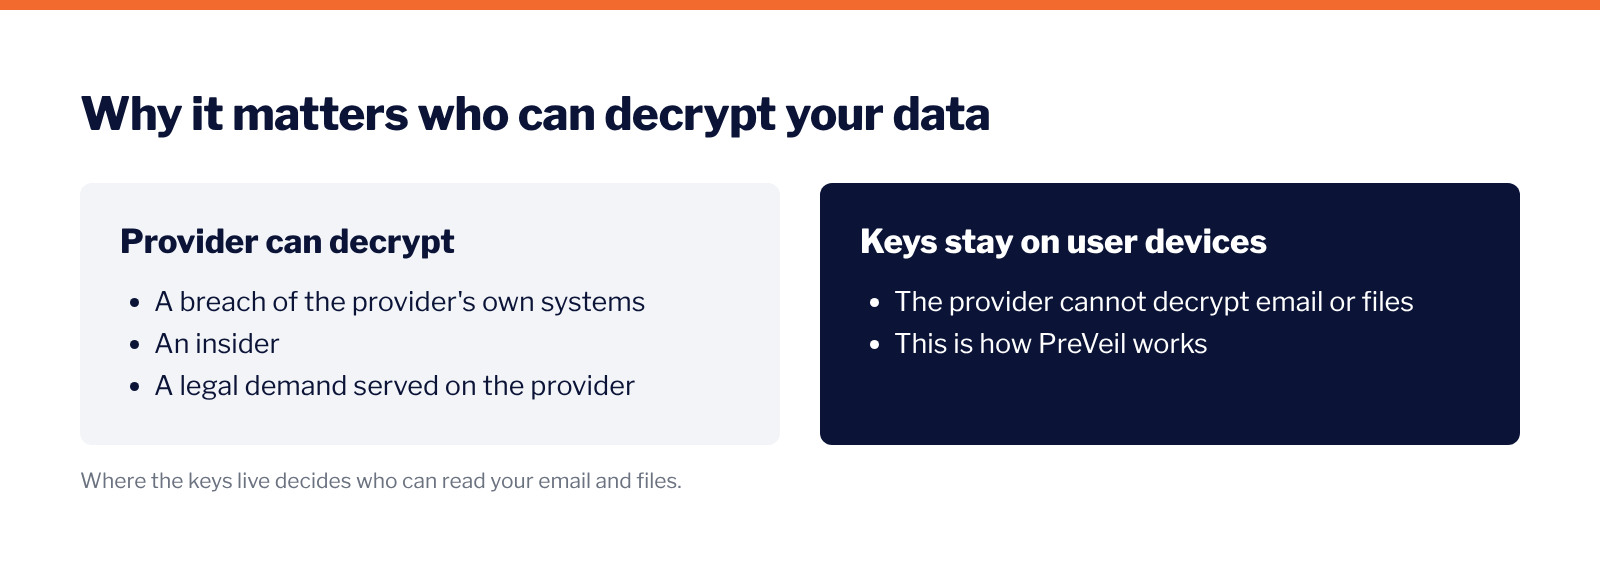
Outlook’s default encryption leaves email exposed to attack. Microsoft 365 uses TLS to encrypt the connection between mail servers, but the message itself sits on Microsoft’s servers in a form Microsoft can read and arrives readable in every mailbox it reaches. Microsoft also holds the keys for its Message Encryption option. Anyone who breaks into those servers, or takes those keys, can read the mail.
In 2023, attackers used a stolen Microsoft signing key to read Exchange Online email at about 25 organizations, including government agencies. AI is now making attacks on servers faster and cheaper: in May 2026, Google reported the first zero-day exploit it believes was developed with AI, and in November 2025, Anthropic reported a state-sponsored campaign that used AI for 80 to 90% of the work.
For anyone in a regulated industry, or anyone who needs to keep their data private, the question that matters is who holds the keys. This guide covers Outlook’s built-in options, how to send with each, and where they stop.
What encryption options does Outlook offer?
Microsoft 365 offers three ways to encrypt email in Outlook. They differ on whether a message stays encrypted after delivery, who can decrypt it, and what the recipient has to do. Facts below come from Microsoft’s own documentation as of October 2026.
✓ the vendor’s own page confirms it · ◐ partly · ✗ the vendor’s own page shows otherwise · – not stated on the pages reviewed (October 2026)
TLS: Microsoft 365 uses Transport Layer Security to encrypt the connection between two servers. It protects a message in transit, and Microsoft’s documentation notes that once the message is received it is transformed back into readable plain text.
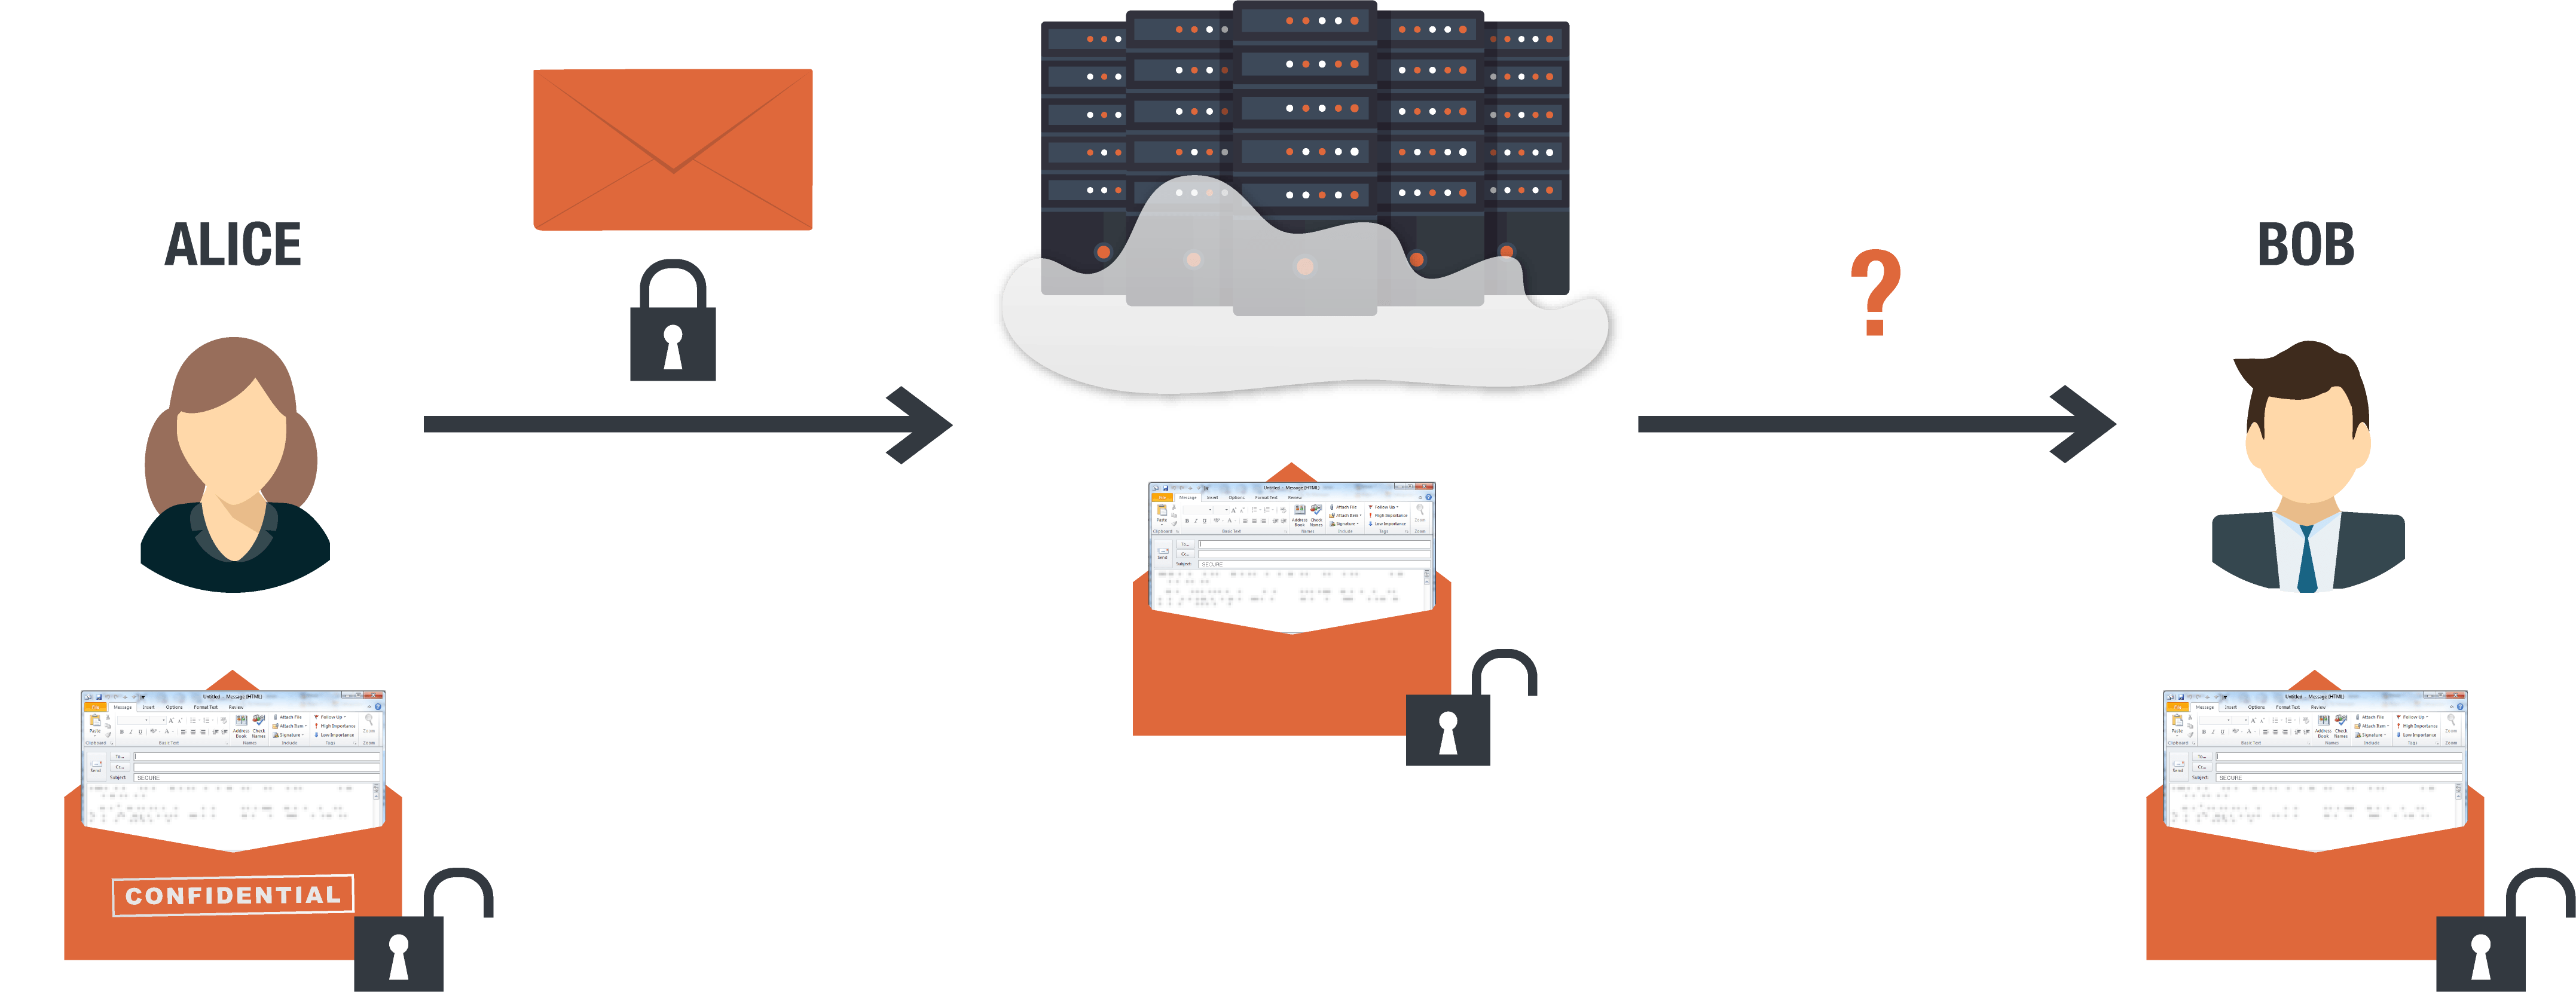
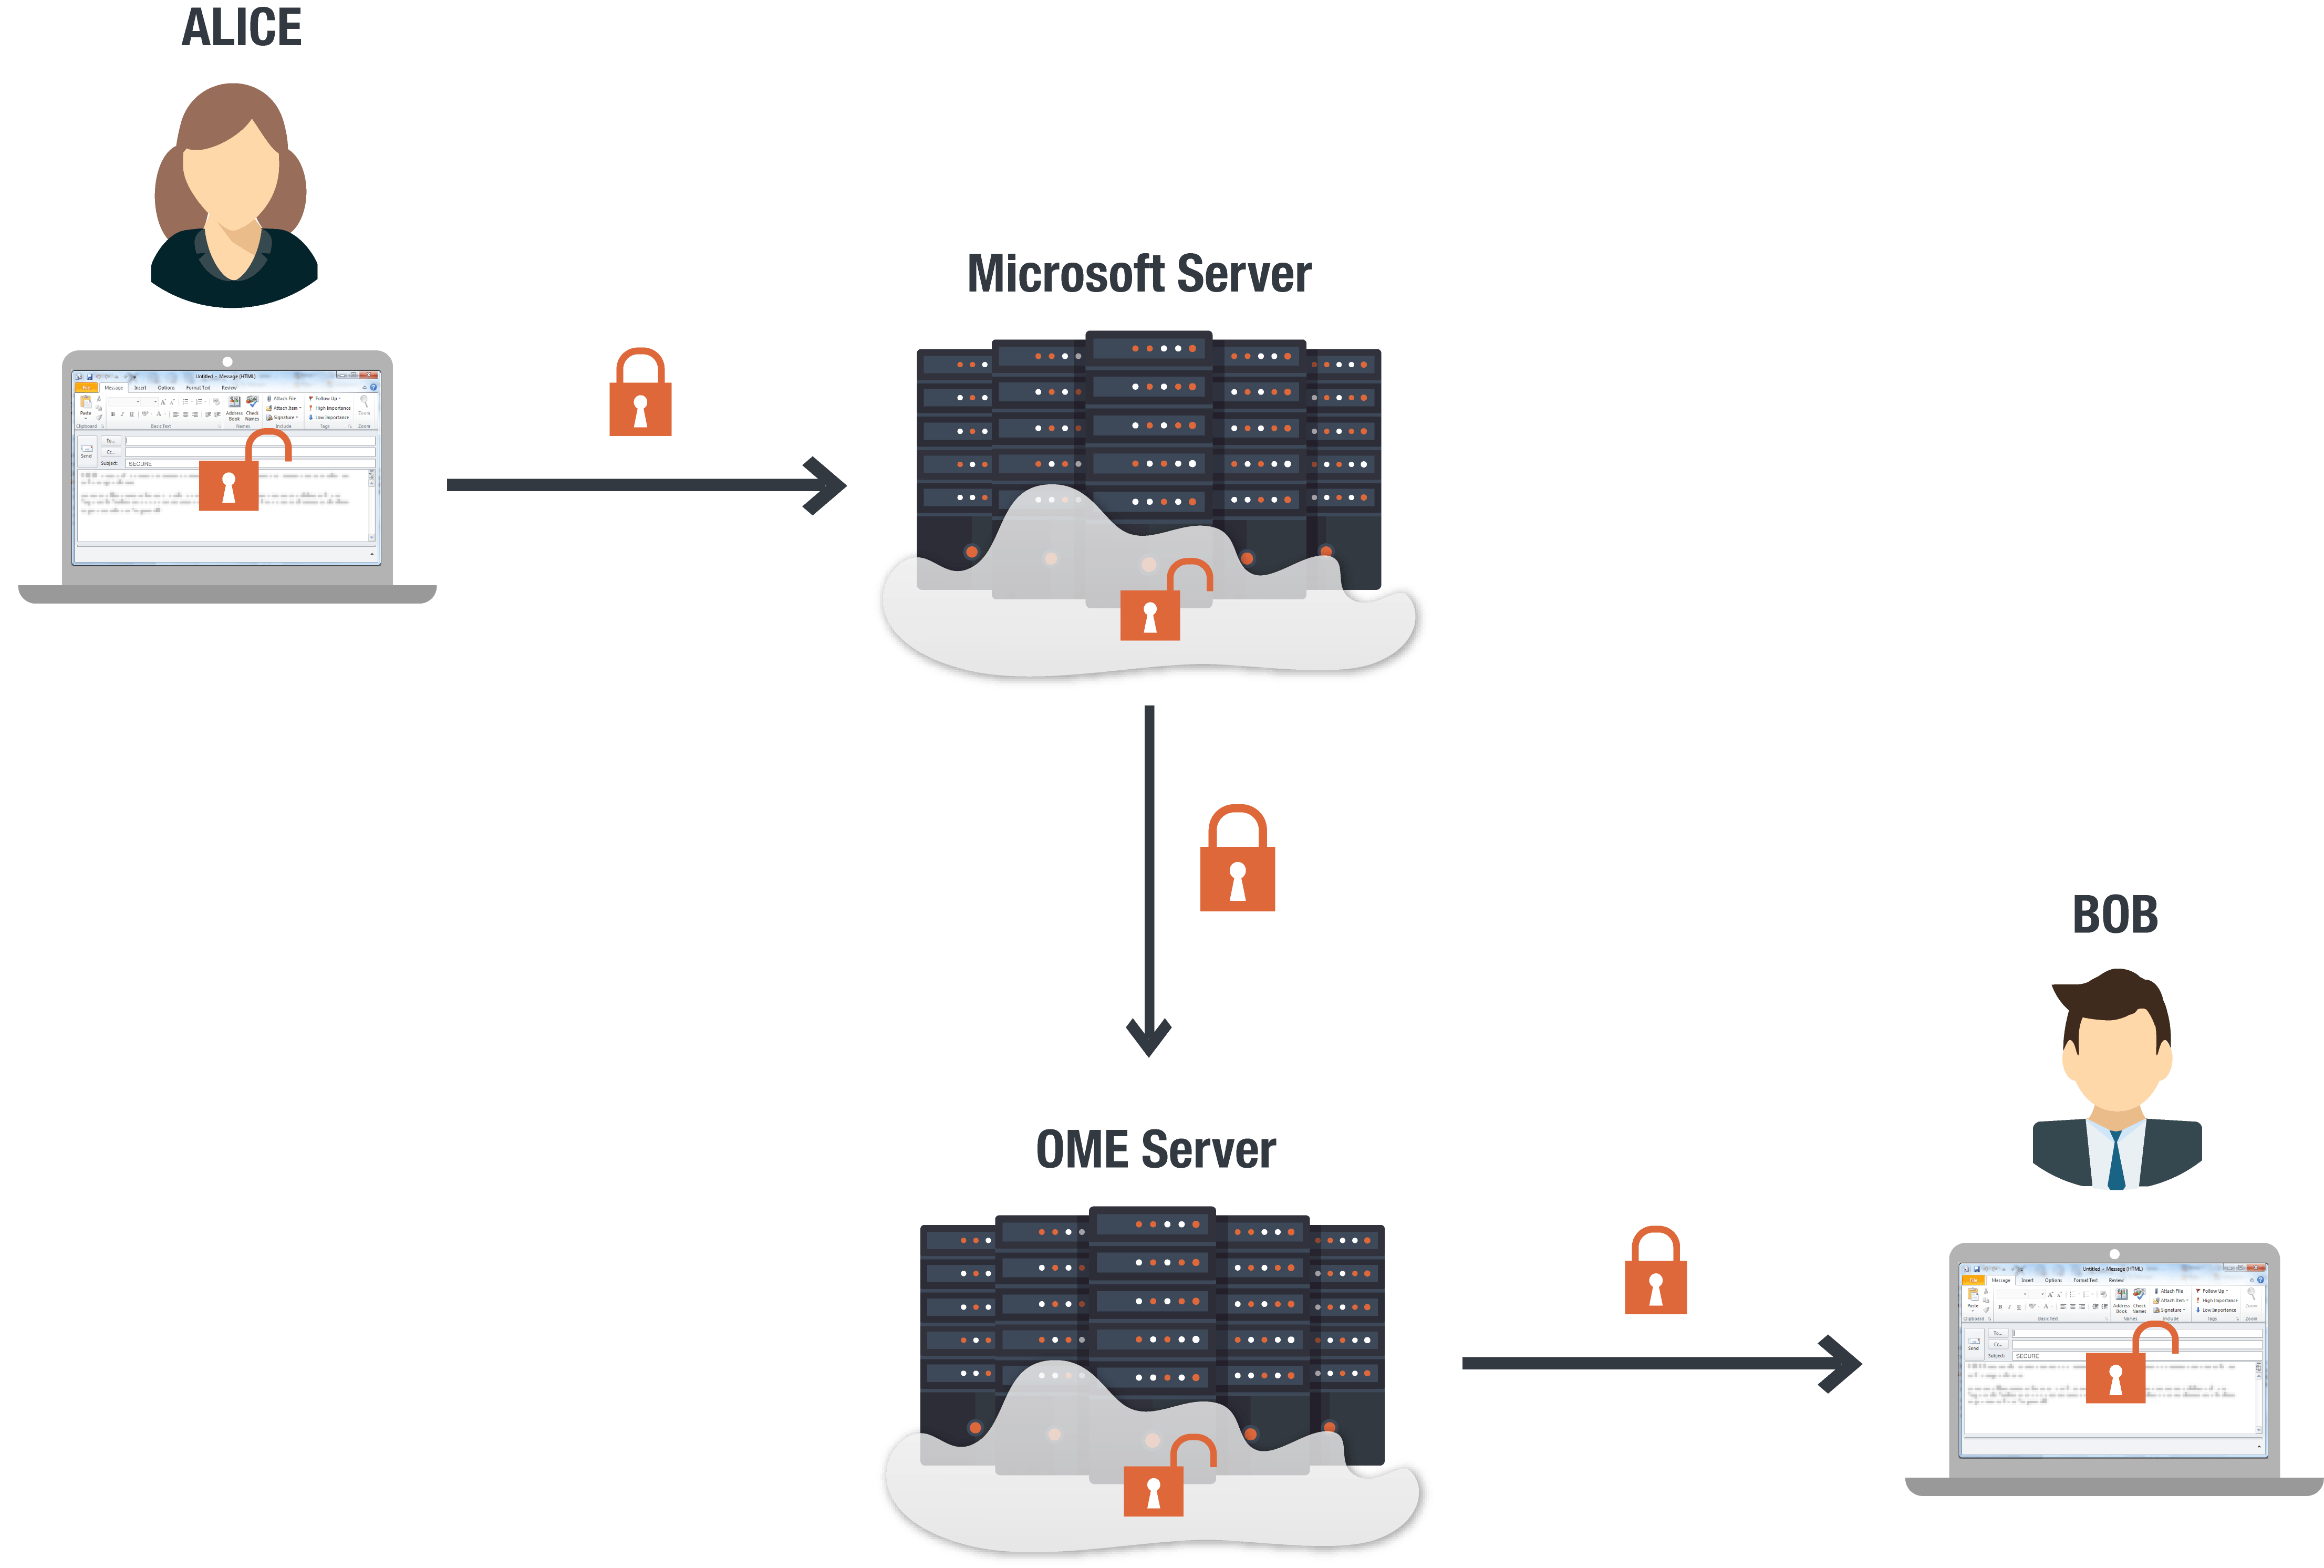
Microsoft Purview Message Encryption: Message Encryption sends encrypted email to people inside or outside the organization. Recipients outside Outlook open it with a one-time passcode or a Microsoft account, and Microsoft writes that it “securely manages and stores the keys.”
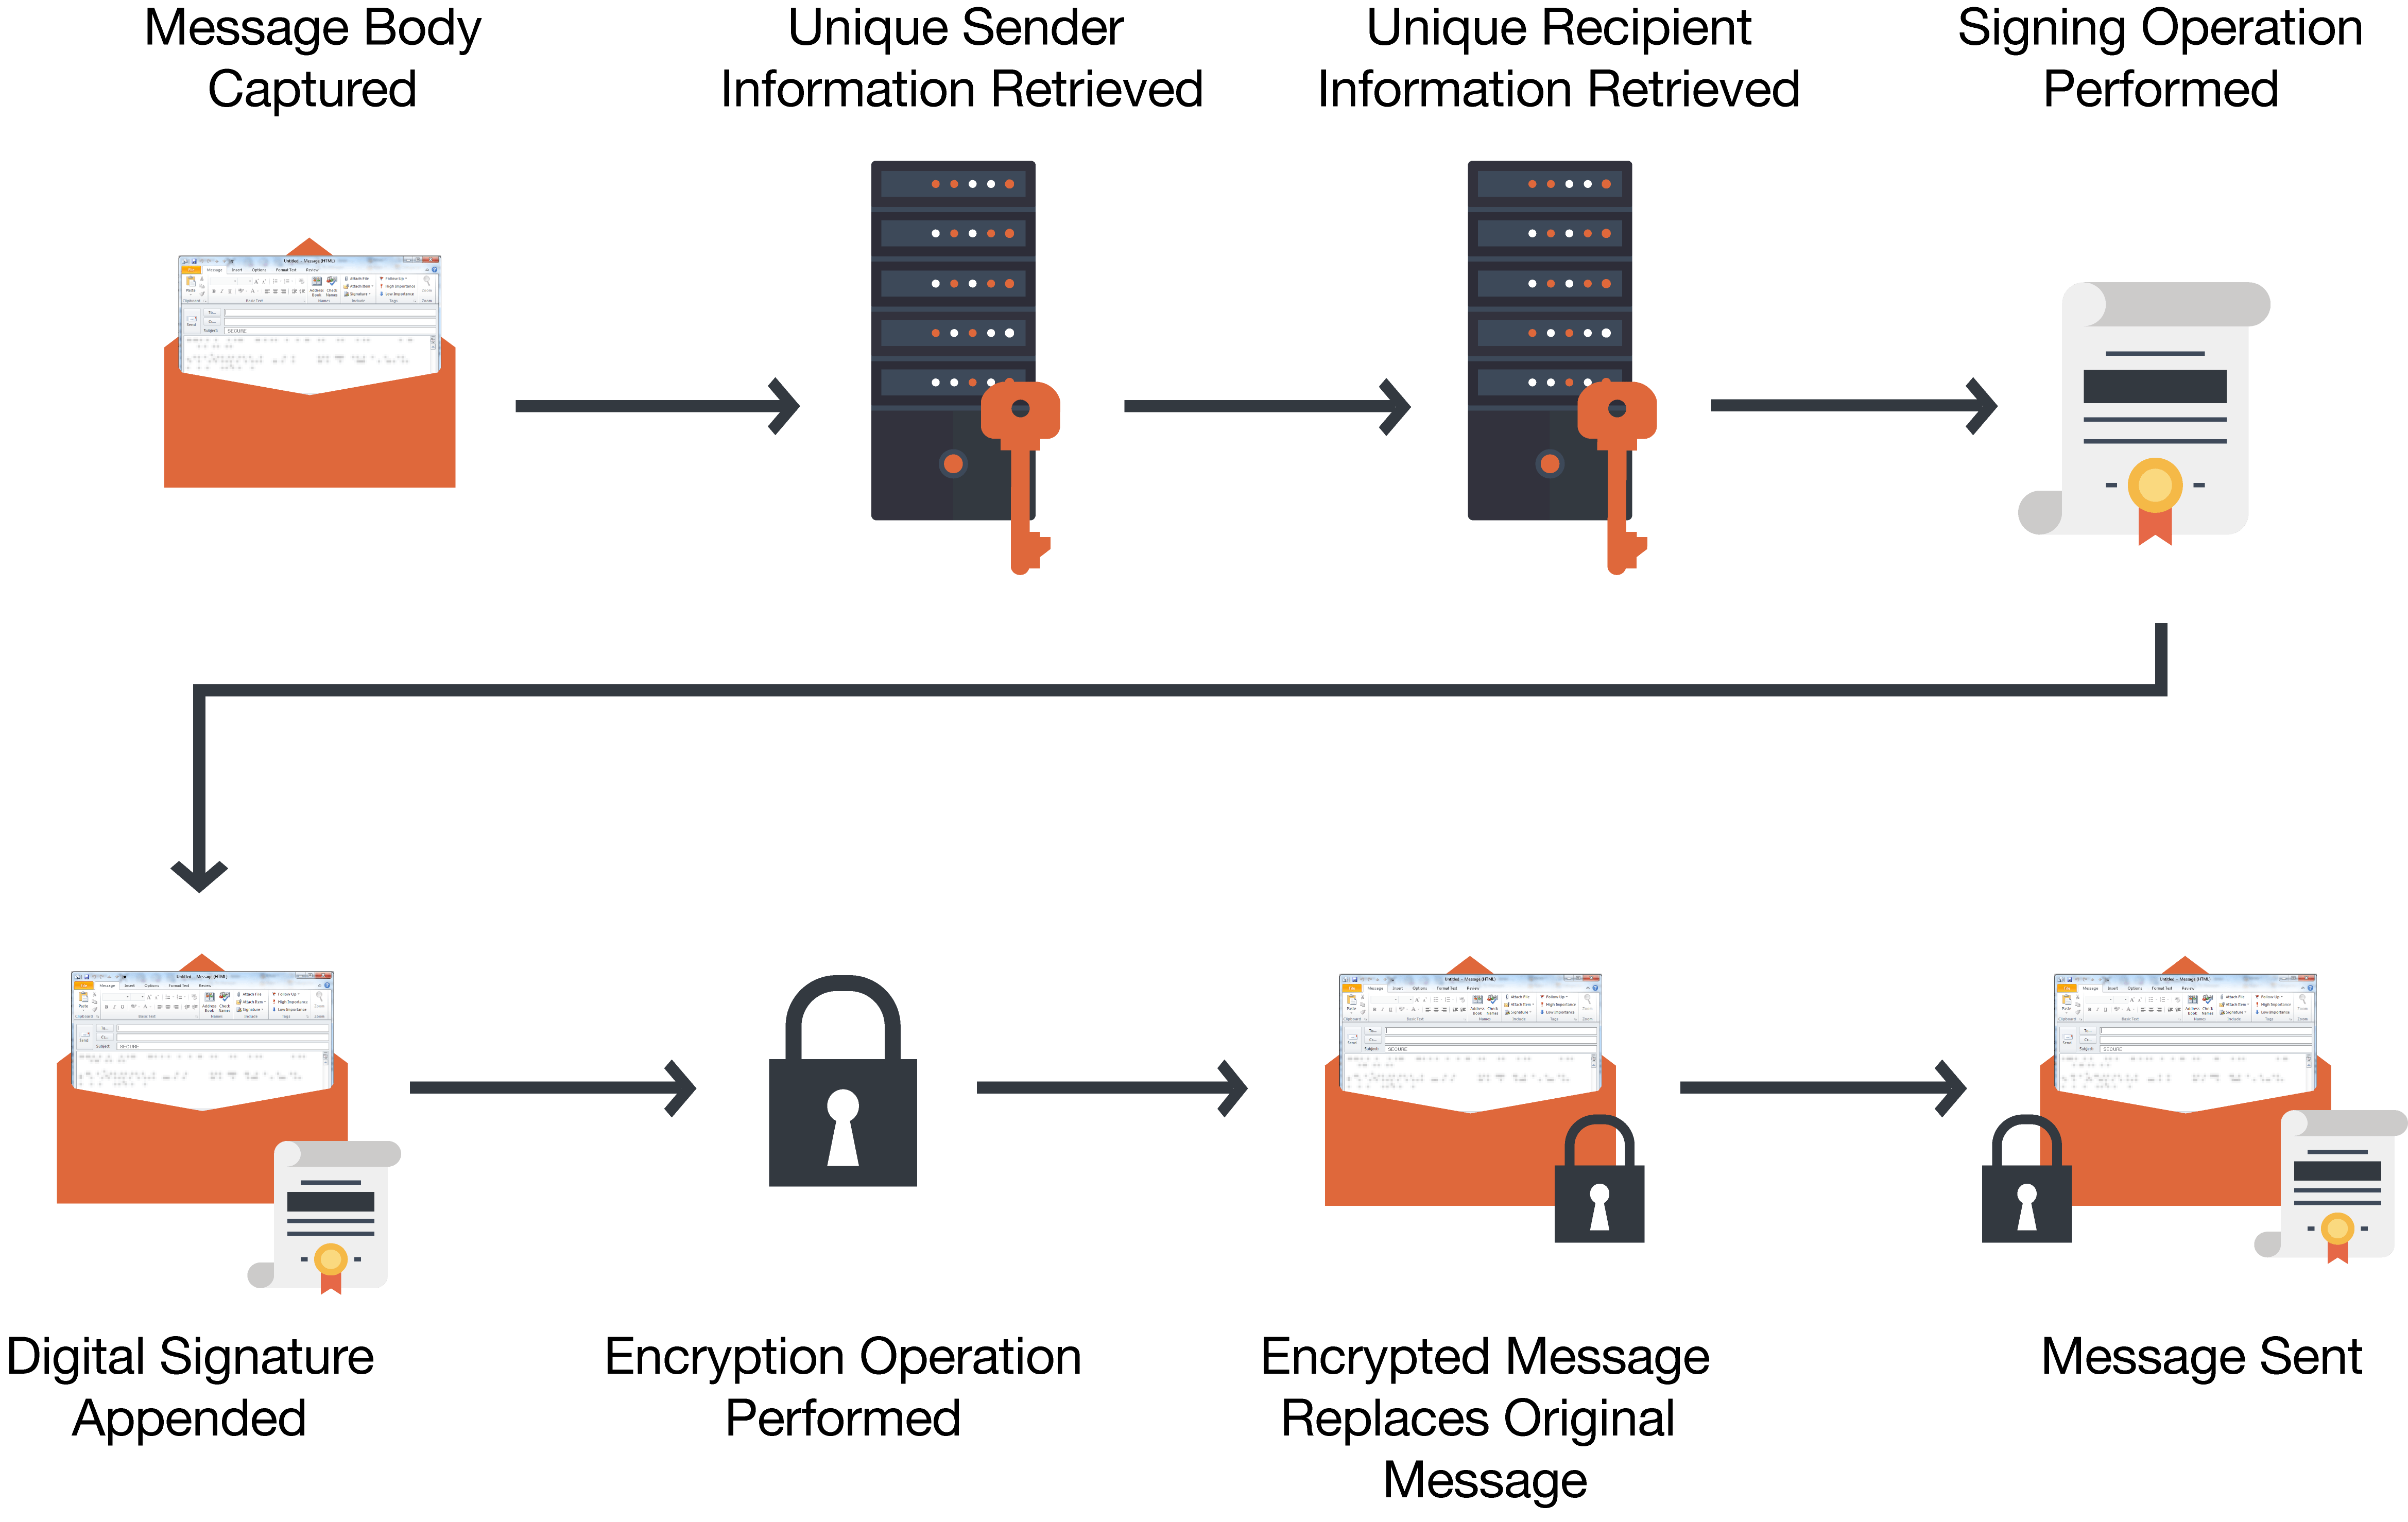
S/MIME: S/MIME encrypts and signs messages with certificates, so only the intended recipient can open them. Every recipient has to maintain a private key, and the sender needs each external recipient’s certificate installed, which rules it out for most email with clients and partners.
How do you send an encrypted email in Outlook?
TLS: Needs no action. Microsoft 365 applies it automatically.
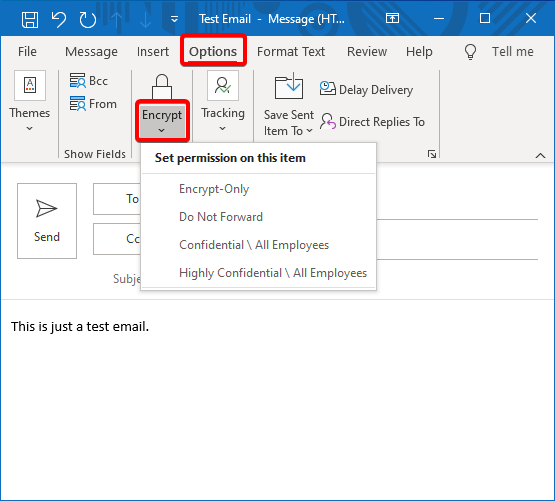
Microsoft Purview Message Encryption: Open a new message, select Options, then Encrypt, and choose Encrypt-Only or Do Not Forward. In the new Outlook, the first option is labeled Encrypt. Administrators can also set mail flow rules in the Exchange admin center that encrypt messages automatically, for example everything sent outside the organization.
S/MIME: Outlook first has to be set up with certificates. Then select Options, More Options, and check Encrypt this message (S/MIME). Microsoft’s guide to sending encrypted email in Outlook has the full steps for both.
PreVeil: Add PreVeil to Outlook and send from your encrypted inbox there. Message contents and attachments are encrypted on your device before they leave it.
Is Outlook encryption enough for regulated industries?
Most rules that cover sensitive data ask who could reach it, not only whether it was encrypted. The table maps the main ones to how PreVeil supports each.
PreVeil works inside Outlook and encrypts message contents and attachments end to end. The encryption keys stay on users’ devices, so PreVeil cannot read the email it stores or sends. PreVeil signs a BAA, keeps activity logs in the admin console on the Business plan, and deploys in hours. More than 3,000 organizations use PreVeil, and PC Magazine named it an Editors’ Choice.
See PreVeil inside your Outlook
A demo shows end-to-end encrypted email inside Outlook, with encryption keys that stay on your users’ devices.
Frequently asked questions about encrypting email in Outlook
Does Outlook encrypt email by default?
Microsoft 365 uses TLS by default to encrypt the connection between mail servers. TLS does not encrypt the message itself, and once the message is received it is readable plain text.
Can Microsoft read email sent with Microsoft Purview Message Encryption?
Microsoft writes that it securely manages and stores the keys for Message Encryption, so Microsoft’s service holds what it needs to decrypt the content. With PreVeil, the encryption keys stay on users’ devices, so PreVeil cannot decrypt message contents or attachments.
What do recipients need to read encrypted Outlook email?
With Message Encryption, recipients outside Outlook use a one-time passcode or sign in with a Microsoft account. With S/MIME, each recipient needs a certificate. PreVeil recipients read and reply for free from their browser after a one-time sign-up, and their replies stay encrypted.
Is Outlook encryption enough for HIPAA, the FTC Safeguards Rule, CMMC or ITAR?
Those rules ask who can reach the data as well as whether it was encrypted. With Outlook’s default options Microsoft holds the keys. PreVeil adds end-to-end encryption inside Outlook with keys on users’ devices, signs a BAA, keeps activity logs on the Business plan, and uses a FIPS 140-3 validated cryptographic module.
Related reading
- How to encrypt Gmail
- End-to-end encryption: what it is and how it works
- Public and private keys: why it matters who holds them
- Is Outlook or Gmail encryption enough for the FTC Safeguards Rule?
- Is Gmail HIPAA compliant? Gmail, Google Workspace and Microsoft 365 compared
- Does encrypting email in Outlook or Gmail protect privileged client communications?
- PreVeil for regulated industries

